

How it works
Cyber tests two surfaces. A test run dynamically tests the running app; a Code Audit reads the source behind it. A test run goes like this:
A Code Audit skips steps 1 to 3: you pick a connected repository and its release branch, and the audit scans the code, investigates what it finds, and verifies each candidate against the commit it pinned. It then monitors that branch, auditing it every day or on every push, and watches the branch’s libraries for new advisories.
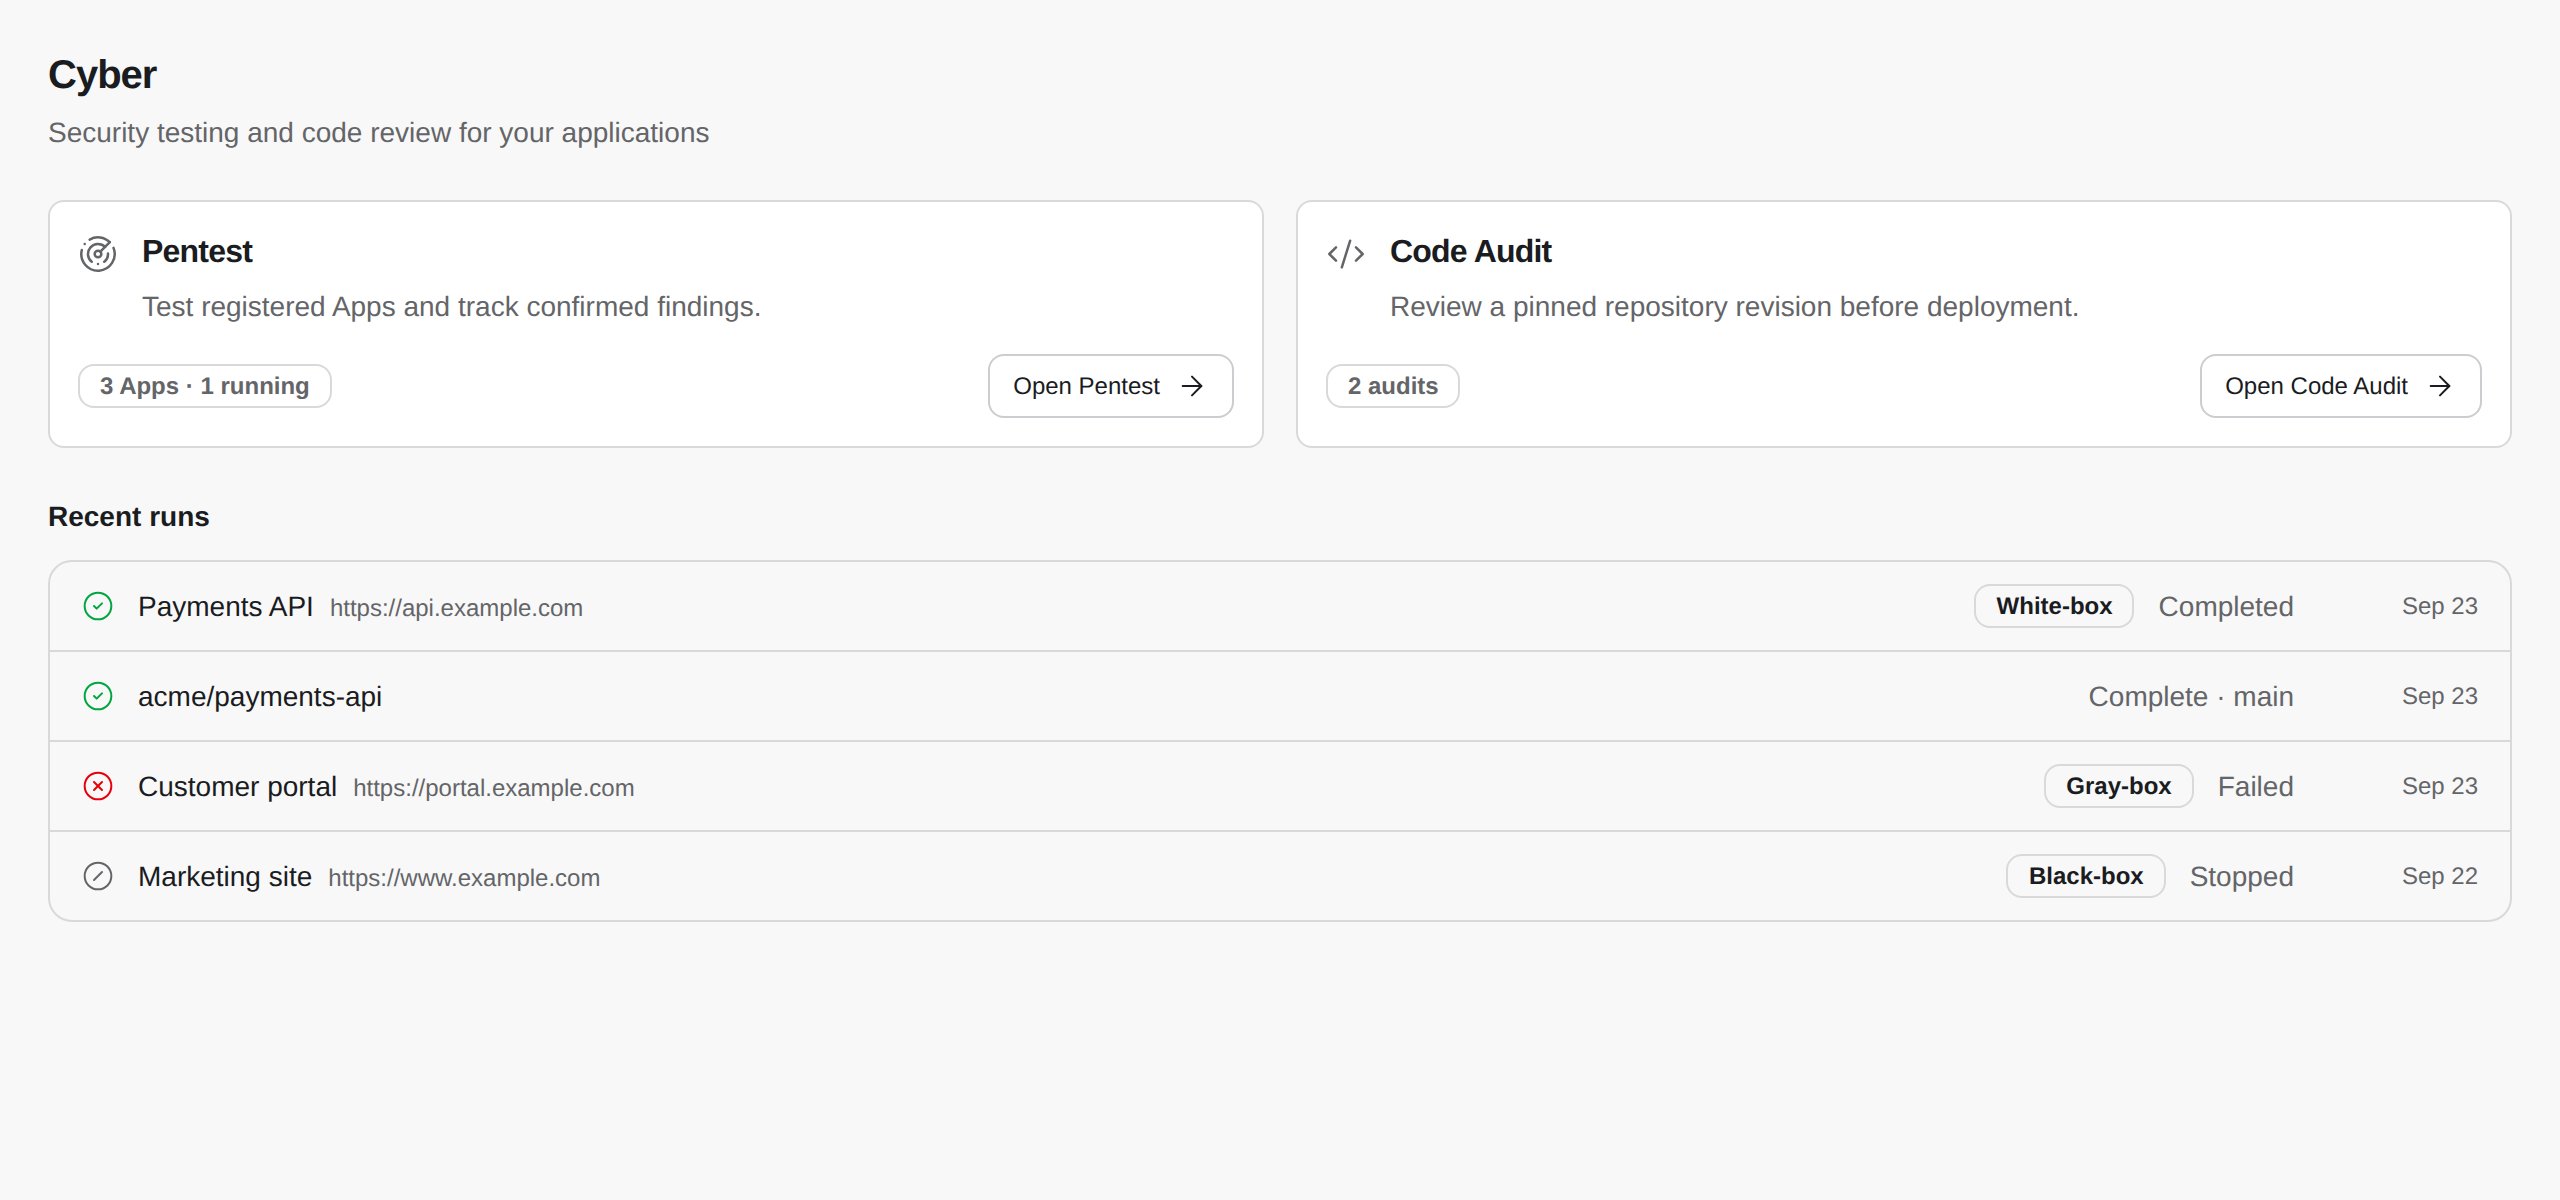
Click Cyber in the sidebar to open the overview: your apps, their latest results, and recent activity. The sidebar holds Overview, Pentest, Code Audit, Findings, and Settings. Code Audit lists the repositories it monitors.
Safety model
Cyber sends real test traffic to your app, so every run is fenced in by settings you control: the target, the paths it may touch, the test users it signs in as, and how hard it pushes.Before your first run
Settle these with your platform team before you launch, so the run isn’t blocked or paged on.What you can do
Key concepts
Get started
Cyber quickstart
Run your first test against a staging app
Run a security test
Set up test users, scope, intensity, and schedules
Triage findings
Read the proof, fix, and retest
Run a Code Audit
Audit a repository branch and follow it across commits